
Things I broke
CVE‑2024‑21388
A hidden marketing API in Microsoft Edge that let a web page silently install any extension, with any permission. No prompt, no click.
- MSRC
- credited CVE · patched in Edge 121
- 0 clicks
- needed to install
- Any permission
- granted silently
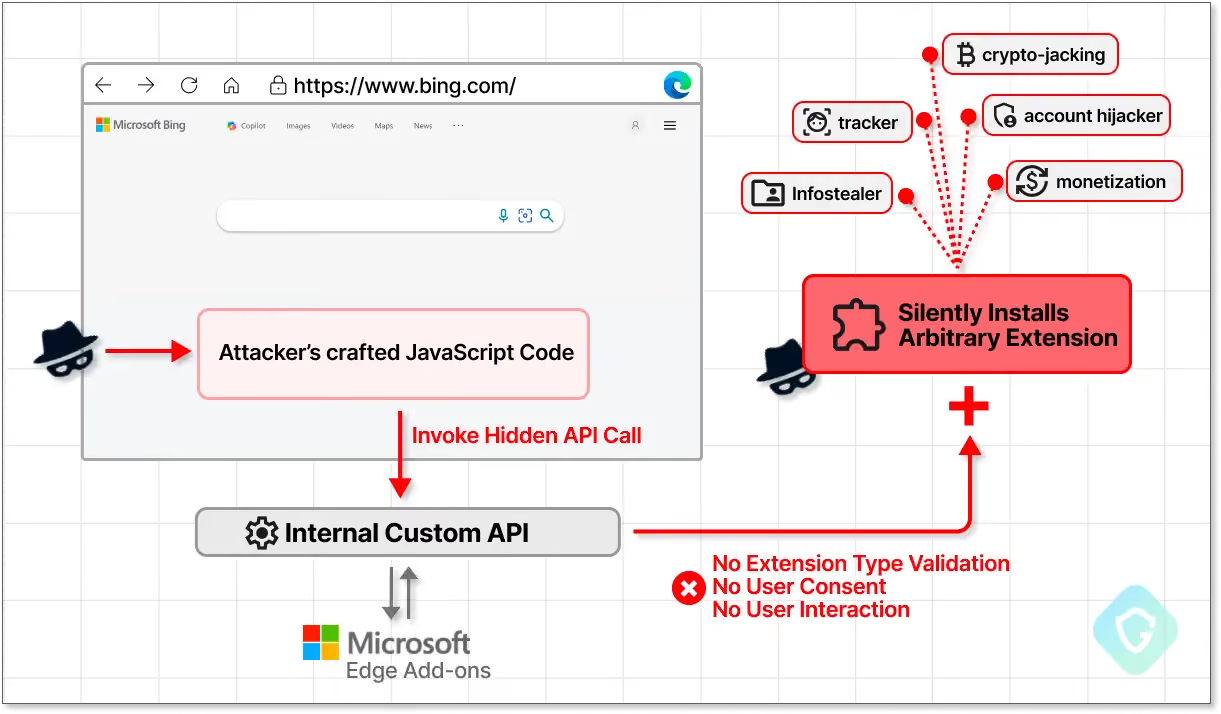
Edge ships with private APIs that only Microsoft’s own sites are meant to call — one of them installs add-ons for marketing campaigns. It didn’t check what it was installing.
With a foothold on a single trusted origin, an attacker could quietly install an extension with broad permissions: a keylogger, an ad injector, a crypto-jacker. Microsoft fixed the vulnerability and credited the finding as CVE-2024-21388.
In the press
The Hacker NewsMicrosoft Edge Bug Could Have Allowed Attackers to Silently Install Malicious Extensions TechRadarThis Microsoft Edge security flaw could have allowed hackers to install all kinds of malicious extras - but there's good news MSPowerUserMicrosoft patches Edge browser vulnerability that could have led to malicious extension installation
Read the research
MyFlaw