
Threats I hunted
EtherHiding
A novel attack technique hiding malicious code inside Binance Smart Chain and Ethereum smart contracts — creating untakeable command-and-control.
- US HHS
- threat advisory · coined industry term
- Lazarus / UNC5342
- adopted by nation-state actors
- Immutable C2
- tamper-proof malware hosting
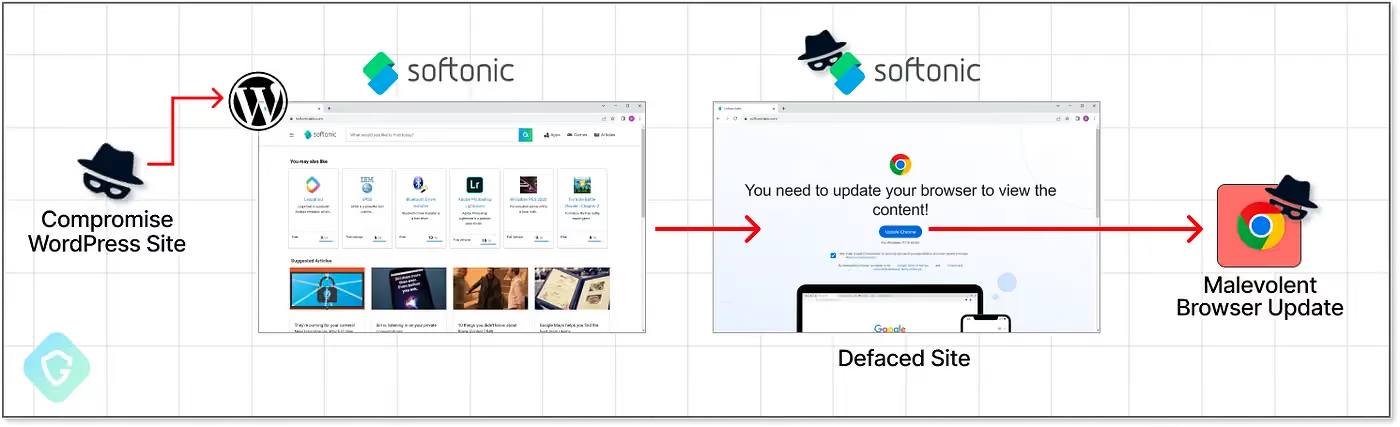
Malicious scripts hosted on conventional servers get taken down quickly by hosting providers. Threat actors bypassed this by storing obfuscated JavaScript payloads directly inside blockchain smart contracts on Binance Smart Chain.
Compromised websites queried the blockchain via public RPC nodes, executing payload updates that defenders could neither block nor seize. After our disclosure, US HHS issued an advisory and Google Mandiant tracked North Korean APT groups adopting the technique.
In the press
BleepingComputerHackers use Binance Smart Chain contracts to store malicious scripts The Hacker NewsBinance's Smart Chain Exploited in New 'EtherHiding' Malware Campaign Google MandiantDPRK Adopts EtherHiding CointelegraphEtherHiding: Hackers create novel way to hide malicious code in blockchains Protos‘EtherHiding’ hack uses Binance blockchain to extort WordPress users
MrTonyScam