
Threats I hunted
MrTonyScam
A massive Facebook Messenger botnet targeting 100,000+ business accounts weekly with Python infostealers disguised as PDF invoices.
- 100K+
- business accounts targeted weekly
- 1 in 70
- infection rate observed
- Vietnam
- threat actor syndicate traced
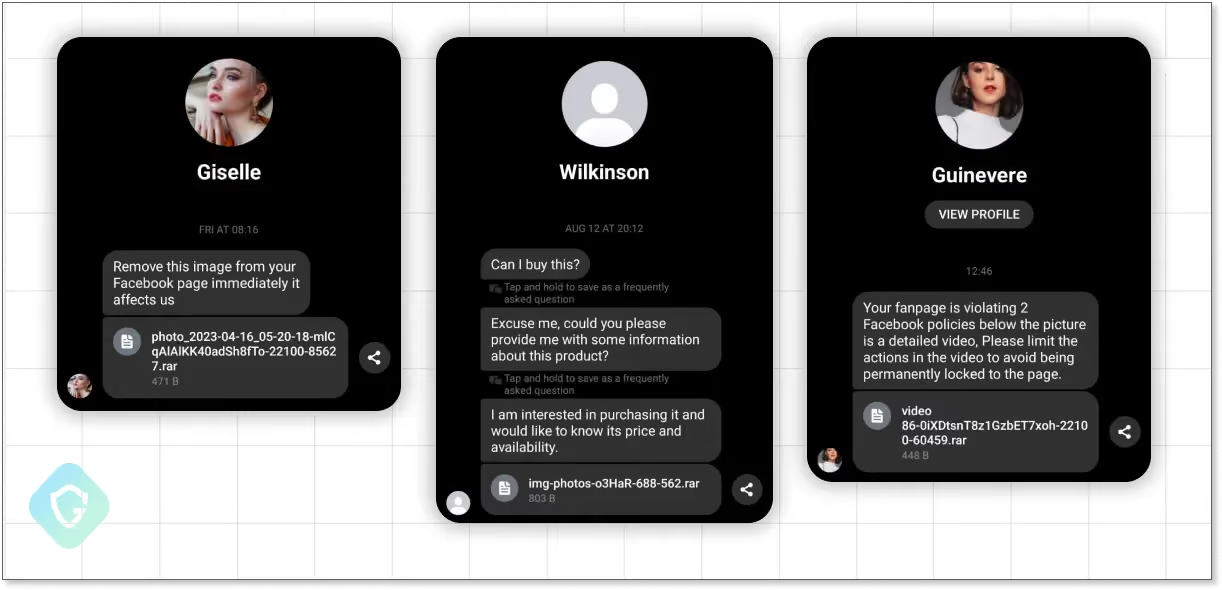
Hijacked personal Facebook accounts were weaponized to blast corporate pages with urgent inquiries containing malicious PDF attachments. The campaign targeted social media managers and marketing teams.
Opening the file launched a multi-stage Python infostealer designed to steal session cookies, Facebook Ads manager credentials, and cryptocurrency wallets. We mapped the infrastructure and attribution back to a cybercrime syndicate in Vietnam.
In the press
BleepingComputerFacebook Messenger phishing wave targets 100K business accounts per week Dark ReadingMillions of Facebook Business Accounts Targeted by Python Malware Tom's GuideHackers are using Facebook Messenger to spread password-stealing malware — how to stay safe SC MediaFacebook Messenger exploited in phishing campaign aimed at business accounts CPO MagazineFacebook Messenger Phishing Campaign Targets Millions of Business Accounts Locking Out Owners
Read the research
CVE‑2024‑21388